MSc UK SME Cyber and ICO-Facing Practice
ICO complaints, ransomware, and SME controls—not CISSP and not a hacking course.
Conferred under the Polish Law on Higher Education with European ECTS Diploma Supplement.
ApplyAcademic Overview
SMEs do not fail cyber because they lack a Silicon Valley SOC; they fail because backups were a myth, MFA was optional, and nobody owned the ICO clock. This MSc starts there. You will map a ransomware weekend for a ten-person firm, write a personal-data inventory that is not a lie, and brief a director without claiming a hacking qualification. Polish and rUK SMEs sit in the cases: professional services in Warsaw, manufacturers in the Central Belt, care and education suppliers who hold children’s data. Dual-pathway students sit the same assessments. Faculty mark whether you can separate UK GDPR, PECR, and NIS-adjacent duties without dumping a US NIST poster as the whole answer. The degree is not CISSP, not a penetration-testing licence, not ICO employment. Offensive techniques are not taught as a curriculum outcome. Capstones must improve a control environment, not demonstrate intrusion. ICO-facing clocks, children’s data in small education suppliers, and invoice-fraud on a Friday afternoon are the Polish and UK cases, not a Silicon Valley breach memoir. IU International University of Applied Sciences will not display NCSC, ICO, or CISSP marks. You will still be expected to brief a director in plain English about residual risk after MFA and backups are real rather than slideware. MSc UK SME Cyber and ICO-Facing Practice is taught as one award, not a list of unrelated modules. The published length is 18 months, and the credit total is 36. Students move from UK GDPR and PECR for SME Operators through UK GDPR and PECR for SME Operators; ICO Processes, SARs, and Complaint Clocks; NIS-Adjacent Duties without Operator Theatre; Identity, MFA, and Backup Reality; Phishing, Invoice Fraud, and Staff Culture; Cloud, Laptops, and Home Working in SMEs, and finish on Tabletop Exercises that Are Not LARP Hacking. Each course has a question, a method, and a submission. In this field, students map one named system, write a threat model, and specify the controls that would stop the most likely path. Reading is control catalogues, incident write-ups, and a short technical standard. The artefact a marker expects is a defensive design with a test plan and a statement of residual risk. The award is built so that a graduate can do the following in practice: Design proportionate SME controls and backup reality tests Run an ICO-facing complaint or SAR timeline as operations Write an incident log a director and an insurer can read Teaching assumes the student can read a source, attempt a problem before the seminar, and revise after feedback. Attendance at live seminars is part of the design. The capstone or final course must use the methods of the earlier courses; a project that ignores them does not pass. The pages for each course name the topics that are examined. Those topics are the syllabus. A brochure line is not a substitute for them.
The degree is awarded directly by IU International University of Applied Sciences, seated in Warsaw, Poland. Studies are conducted in full alignment with Polish and European academic standards.
Curriculum & Core Modules
The curriculum comprises 36 ECTS credits structured across progressive academic modules:
UK GDPR and PECR for SME Operators
ICO Processes, SARs, and Complaint Clocks
NIS-Adjacent Duties without Operator Theatre
Identity, MFA, and Backup Reality
Phishing, Invoice Fraud, and Staff Culture
Cloud, Laptops, and Home Working in SMEs
Ransomware Weekends and Honest Downtime
Insurers, Solicitors, and Notification Decisions
Teaching & Assessment Methodology
Online Pathway
Asynchronous learning via the university LMS, digital library access, faculty-led virtual seminars, and proctored online assessments.
Warsaw Campus Pathway
In-person lectures, tutorial seminars, and laboratory sessions at Prosta 20, Warsaw, with full campus facility access.
Career Trajectories
- SME cyber and compliance lead (academic MSc; not CISSP)
- Office/operations manager with data-protection ownership
- Incident coordinator in a small organisation
- Supplier-risk officer
- DPO support analyst (appointment not conferred)
European Campus & Academic Facilities
Seated at Prosta 20 in Warsaw, IU International University of Applied Sciences offers state-of-the-art academic lecture halls, digital research repositories, and vibrant collegiate spaces for both on-campus and international distance scholars.
Main academic building at Prosta 20, Warsaw.
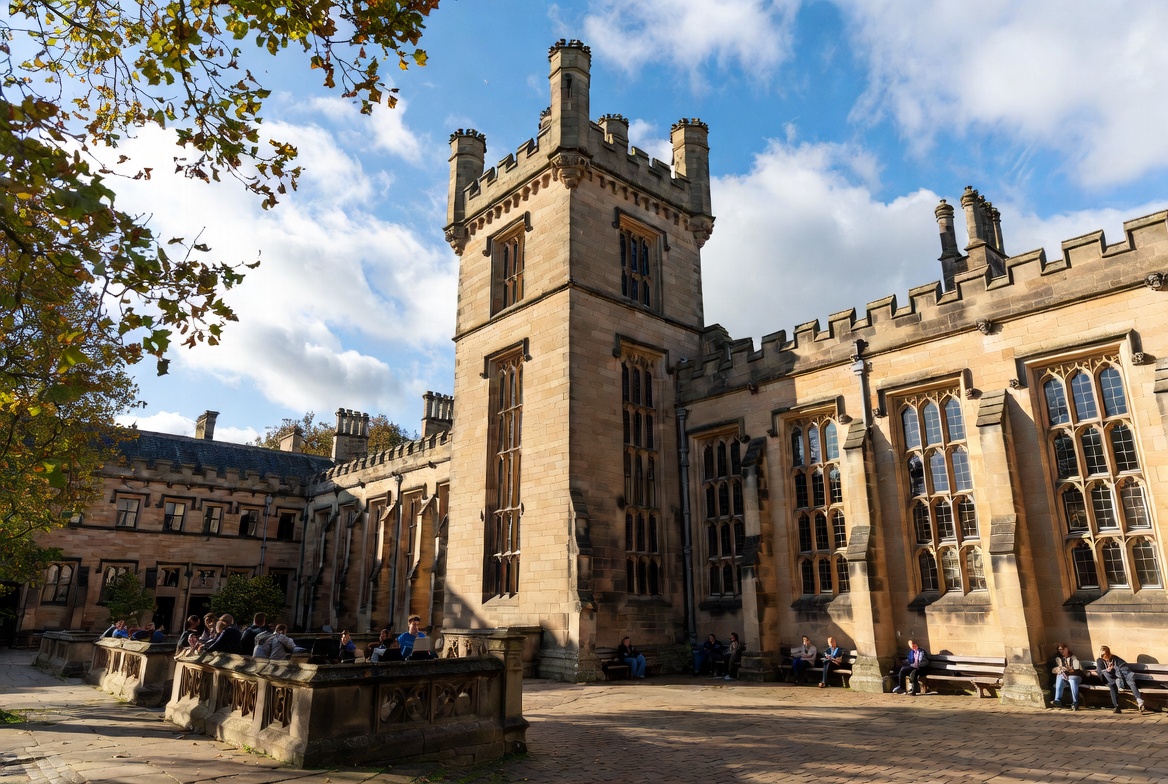
Collegiate courtyard and research study spaces.
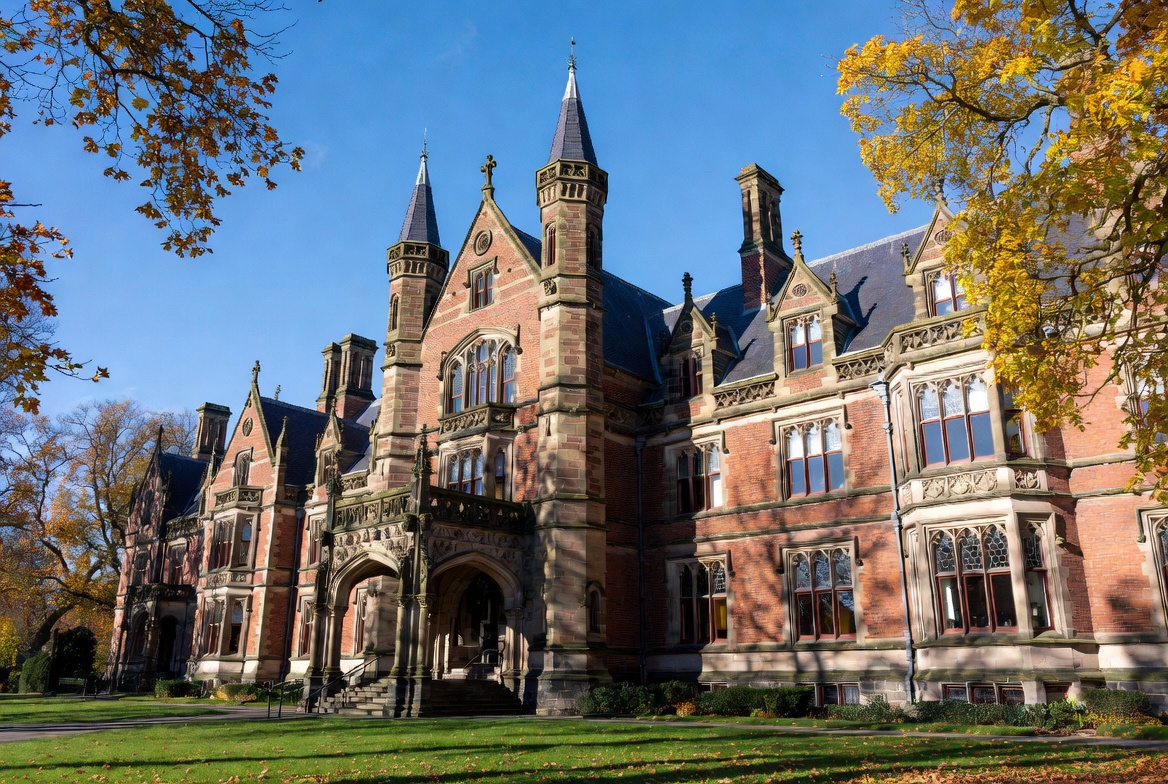
Academic facilities and faculty laboratory suites.
Degree Recognition, NAWA & EDINAC Accreditation
Degrees from IU International University of Applied Sciences are awarded under the statutory framework of the Republic of Poland and the European Bologna Process (ECTS). Qualification transparency and international academic mobility are supported within the framework of NAWA (Polish National Agency for Academic Exchange) and European ENIC-NARIC networks. Furthermore, the university holds Tier 1 Full International Accreditation from EDINAC (Ref: EIAC/QA/PL/2000-IU) with immutable cryptographic diploma verification on edinac.org.